警惕蘋果手機盜U木馬騙局
· 頻道:宝塔搭建包网团队 · 閱讀 15786
1. 近期一個Telegram頻道公開宣稱,其製作的惡意網頁可在蘋果iPhone 13至18系統上停留10秒即完成所謂“盜U”,無需下載、授權或點擊。該說法把攻擊入口包裝成“技術項目”,核心賣點是利用瀏覽器漏洞或系統缺陷竊取加密資產,並強調步驟極簡。對普通用戶而言,任何要求用Safari打開陌生鏈接、停留等待或連接錢包的頁面都應立即關閉;錢包私鑰、助記詞和簽名權限一旦洩露,資產幾乎無法追回。此類“零交互盜U”宣傳往往夾雜誇大和釣魚二次收割,真實攻擊面可能針對舊版系統或特定錢包插件,讀者不應出於好奇測試。
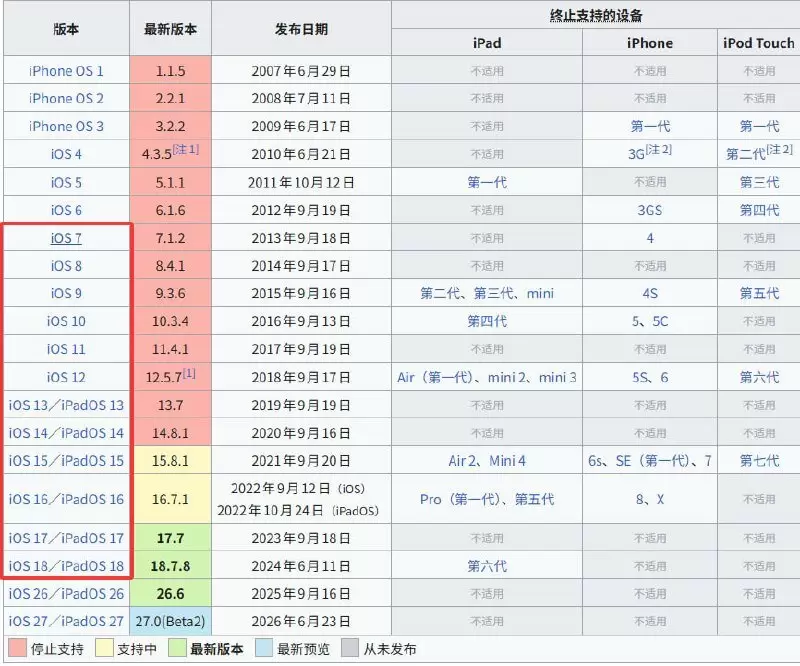
2. 原文內容:項目介紹:這是一款針對蘋果手機盜U的技術,目前已經成功攻破蘋果13-18系統,用戶只需要在我們製作的病毒網站停留10秒,無需下載,無需授權,無需點擊任何...
3. A Telegram channel is promoting a malicious webpage that allegedly steals USDT from iPhones running iOS 13 through 18 after a 10-second visit, with no download, permission prompt, or click required. The claim is a serious red flag: legitimate security research does not advertise turnkey crypto theft. Users should avoid unknown links in Safari, never connect wallets to untrusted pages, and update iOS and wallet apps. Treat such “zero-click” claims as both a threat and a lure for further phishing.
該內容經過二次創作,已經去除違法違規內容。
#網絡安全 #防騙提醒 #蘋果安全 #加密資產安全